Startups move fast. New features roll out, customers sign up, and a small team can quickly grow much larger before processes catch up. Security and compliance often take a back seat to product and revenue, since the risks may not seem urgent at first. But weak foundations are much harder to fix later. As the business grows, access permissions increase, sensitive data spreads, and bigger customers start asking more questions. Laying the right groundwork early isn’t about adding red tape. It’s about making sure growth doesn’t reveal problems that could have been solved from the start.
Know What You Actually Need to Protect
A company can’t protect its information well unless it knows what it has and where it’s stored. Customer records, employee details, financial data, credentials, and intellectual property might all need different types of protection.
Startups need to figure out which systems matter most and how sensitive information moves between them. Cloud services, internal apps, employee devices, and outside tools can all play a role.
This list doesn’t have to be complex. It just helps the company see what might be at risk and where better controls are needed.
Control Access Before It Gets Complicated
Early on, companies often let employees access a lot because everyone does many jobs. This might work with a small team, but it gets harder to manage as more people and systems join.
People should only have the access they need for their work. Regularly checking permissions, using multi-factor authentication, and having clear steps for joining or leaving the company can stop old or unneeded access from piling up.
The aim isn’t to make employees ask for approval all the time. It’s to avoid a situation where nearly everyone can access sensitive systems just because it was simpler when the company was small.
Document the Processes That Matter
Small teams rely heavily on institutional knowledge. One employee knows how access is approved, another handles security concerns, and someone else understands where backups are stored.
This setup gets risky as the company grows. Key processes should be documented so they don’t rely on one person’s memory.
Policies for access, data handling, incident response, vendor management, and security roles help keep things consistent. These policies should match what really happens. A fancy policy that no one follows is less useful than a simple process people actually use.
Treat Vendors as Part of Your Security Environment
Startups rely a lot on outside technology. Payment systems, cloud services, analytics tools, communication apps, and other software might all handle company or customer data.
Every vendor relationship can introduce another place where sensitive information exists. Before adopting a service, teams should understand what data it can access, how it handles that information, and what responsibilities remain with the startup.
Setting up a simple vendor review process early can stop lots of quick software choices from turning into a pile of security risks later.
Prepare for Security Incidents Before They Happen
Security incidents almost never happen at a good time. If something suspicious comes up, not knowing who should respond can make things worse.
An incident response plan sets out who does what ahead of time. Employees should know how to report issues, who checks them, when to escalate problems, and how to keep important information safe.
No plan can cover every situation. The goal is to give the team enough structure to respond calmly, instead of making up a process in the middle of a crisis.
Expect Customers to Ask for Evidence
As startups go after bigger customers, security expectations usually get more formal. Potential clients might send long questionnaires, ask about controls, or want outside proof of how systems and processes work.
Understanding SOC Examination services can help startups recognize how controls may be independently evaluated and reported. More importantly, it highlights why readiness can’t always be created immediately before a customer requests evidence.
Controls need to exist in practice, not just on paper. Building them earlier can make future compliance efforts less disruptive because the company isn’t redesigning its security program while trying to close an important deal.
Choose Compliance Based on Actual Business Needs
Sometimes startups chase certifications or reports just because competitors have them. This can waste time and money if those requirements don’t fit the company’s services, customers, or rules.
The better question is what the business genuinely needs to demonstrate. A comprehensive guide for startups examining SOC reporting can help teams understand the purpose of particular reports before deciding whether they fit their situation.
Compliance should help meet real business needs. It shouldn’t be a bunch of badges collected without understanding why they matter.
Security Culture Needs to Scale With the Company
Technology alone can’t keep a business safe. Employees still choose how to share information, handle credentials, and report anything suspicious.
Security training should relate to real situations employees face. People need to know what’s expected and where to turn if something doesn’t seem right.
It’s easier to build good habits when the company is small. When security is part of daily work, new hires join a place where responsible behavior is already the norm.
Build the Foundation Before Growth Tests It
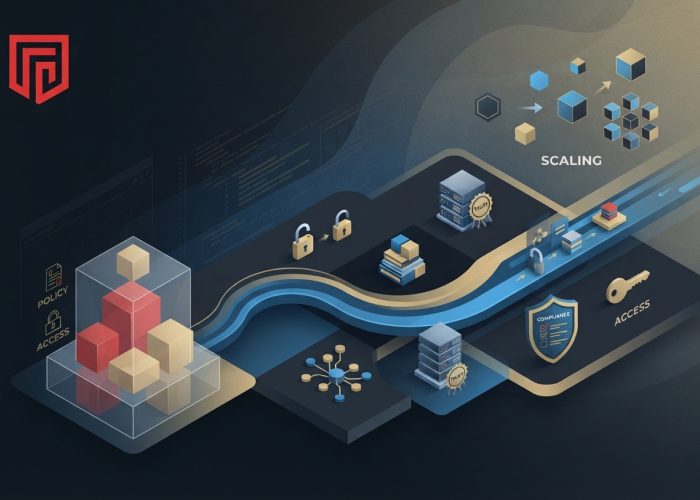
Startups don’t need enterprise-level security complexity from day one. They do need foundations that can evolve as the company grows and takes on more information.
Know where sensitive data lives, control access thoughtfully, document important processes, review vendors, and prepare for incidents. Just as importantly, understand which compliance expectations actually apply to the business.
None of these steps can eliminate every security risk. They can make growth more manageable by preventing security and compliance from becoming emergency projects later. Scaling already creates enough difficult problems. Protecting the business shouldn’t have to become one of them.